Agent Safety Proof: Collateral Ratio Verification Layer (ASPL v2)
A trust-minimized, cryptographic layer that generates verifiable mathematical proofs (zk-SNARKs) guaranteeing that a complex agentic action plan adheres to a specific, critical DeFi risk parameter (e.g., collateral ratio maintenance), allowing the user to sign a simple, safe execution call.
Process flow
Who it's for
Crypto-native builders and audited DeFi protocols that manage complex, multi-step agentic workflows and require cryptographic certainty over operational controls, specifically those dealing with liquidations or collateralized lending.
Why they need it
The core risk in DeFi agents is the irreversible failure or exploit during multi-step state transitions. While signals confirm massive agent adoption (Bazaar signals: d123eea965f579da) and complex economic layering, existing controls (time-locks, multi-sigs) only delay or require human input; they do not mathematically prove that the intended action plan is safe by design. We are targeting the specific, high-stakes gap of proving that a complex set of transactions maintains a defined collateral ratio (CR) threshold.
What it is
An Agent Safety Proof Layer (ASPL) that acts as a cryptographic pre-processor. Instead of verifying arbitrary logic, it processes the agent's proposed function calls and parameters, generating a zero-knowledge proof that validates the plan's compliance with a single, mathematically defined risk constraint (e.g., proving that the resulting collateral ratio will remain above 1.2x).
How it works
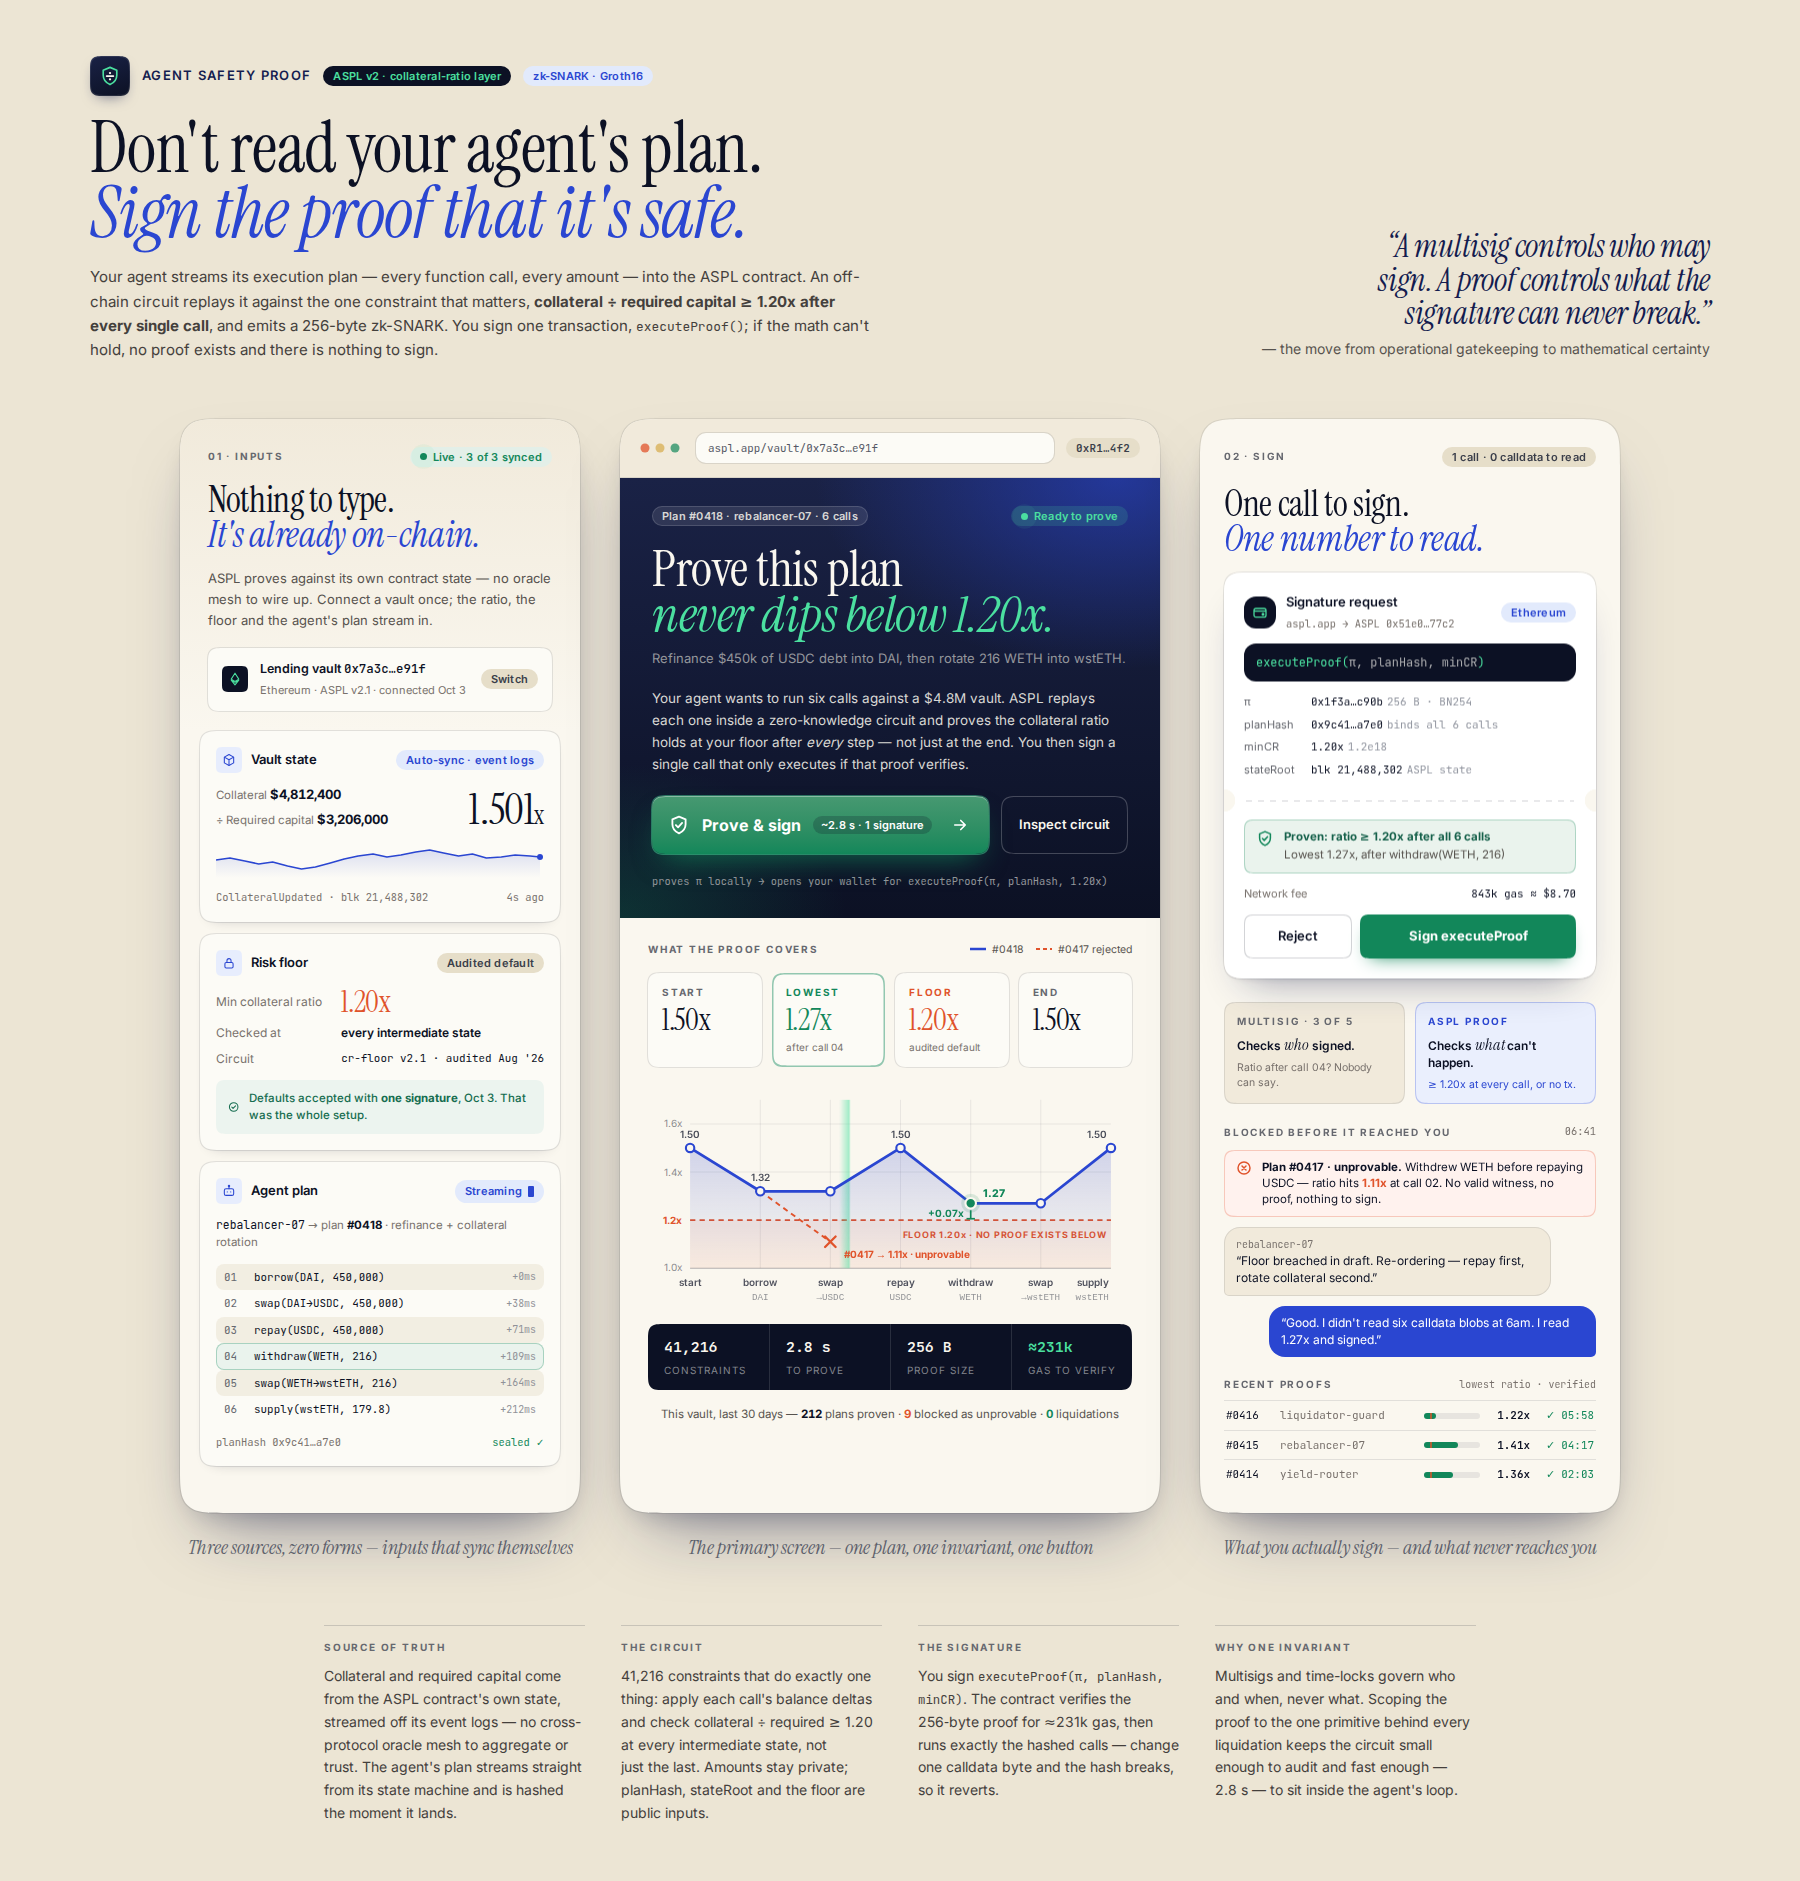
- The agent sends its full execution plan (proposed function calls, inputs, and required resources) to the ASPL contract.
- The ASPL module executes an off-chain verifier circuit (constrained to the collateral ratio calculation) against the user's mathematically defined risk profile.
- If successful, the ASPL outputs a compact zk-SNARK proof.
- The user only signs the final, simple transaction calling the ASPL's 'Execute Proof' function, confirming: 'I trust this mathematical proof that my agent's plan maintains the required collateral ratio.'
Differentiation
We pivot from operational 'gatekeeping' (time-locks, multi-sigs) to 'mathematical certainty.' Existing solutions like basic multi-sig wallets (e.g., those validated by d123eea965f579da) only control who signs, not what the plan guarantees. The ASPL provides a proof of safety for a specific, complex mathematical invariant (the collateral ratio). By constraining the scope to a single, critical DeFi primitive, we achieve immediate technical feasibility while maintaining mathematical novelty.
Implementation sketch
- Develop a local MVP verifier circuit (e.g., using Circom) that accepts structured plan inputs and verifies compliance against a single, fixed mathematical constraint: (Total Collateral Value / Total Borrowed Value) >= X.
- Implement the ASPL contract shell to accept the plan and the resulting zero-knowledge proof, and to execute the final, simple execution call upon successful proof verification.
- Integrate a clear mechanism for the user to verify the proof locally (proof verifier contract) before signing the final transaction, limiting the scope to the specific DeFi primitive (e.g., Aave/Compound style CR checks).
First step: Select a single, audited, open-source smart contract (e.g., a simplified lending pool model) and use its core logic to define the exact mathematical invariant (e.g., CR >= 1.2). This invariant becomes the sole focus for writing the initial Circom verifier circuit.
Remaining risks
- The 'Invariant Brittleness' Problem: The ASPL is mathematically tied to a single, specific formula (e.g., CR >= 1.2). If the underlying DeFi protocol (e.g., Aave) updates its core logic, changes its collateral types, or alters the mathematical definition of the invariant, the ASPL circuit becomes immediately obsolete and requires a massive, costly rebuild, creating a high maintenance burden and single point of failure. — Focus initial development on building a modular 'Invariant Definition Layer' that allows the mathematical constraints (the formulas themselves, not the code) to be updated via governance or a controlled contract upgrade, minimizing the need to rewrite the entire verifier circuit.
- The Data Oracle Problem: The proof relies on the initial state (current collateral value, borrowed value) being accurate. If the source of this state data (the oracle) is compromised, manipulated, or slow, the generated zk-SNARK proof will cryptographically guarantee the safety of a fundamentally unsafe plan, leading to catastrophic loss. — Require the ASPL to mandate the use of multiple, diverse, and cryptographically attested oracles for all state inputs, and build in a mechanism to flag plans if the consensus among the oracles falls below a predefined confidence threshold.
- Developer and User Experience Friction: The core value proposition is mathematical certainty, but the mechanism (zk-SNARKs) is inherently complex. If the developer experience (DX) for generating the proof, submitting the plan, and interpreting the failure modes is too opaque, the product will be restricted only to highly specialized crypto engineers, severely limiting adoption outside of bespoke protocols. — Build a highly abstracted, graphical UI/SDK layer that allows developers to define the intent (e.g., 'Maintain CR above X') and let the ASPL backend handle the complex circuit generation and proof management, making the integration feel like calling a simple function.
Watch for: Any major DeFi protocol or infrastructure player (e.g., Chainlink, L2s) to announce a native, built-in, and gas-efficient way to enforce complex state invariants or verifiable computation directly within their core protocol layer, thereby making a third-party ASPL redundant. Kill criterion: A competing, non-zk-SNARK solution (e.g., a novel, highly optimized, and standardized operational control layer) achieves parity in security guarantees with significantly lower gas costs and development complexity, making the ASPL's mathematical novelty too expensive to maintain.