Asynchronous Resource-Gated Message Protocol (ARGMP)
A standardized, non-blocking message routing protocol that guarantees communication only proceeds if the sender can cryptographically prove resource ownership against a verifiable, asynchronous ledger state.
How can AI agents verify ownership of a resource before trusting a message about it?
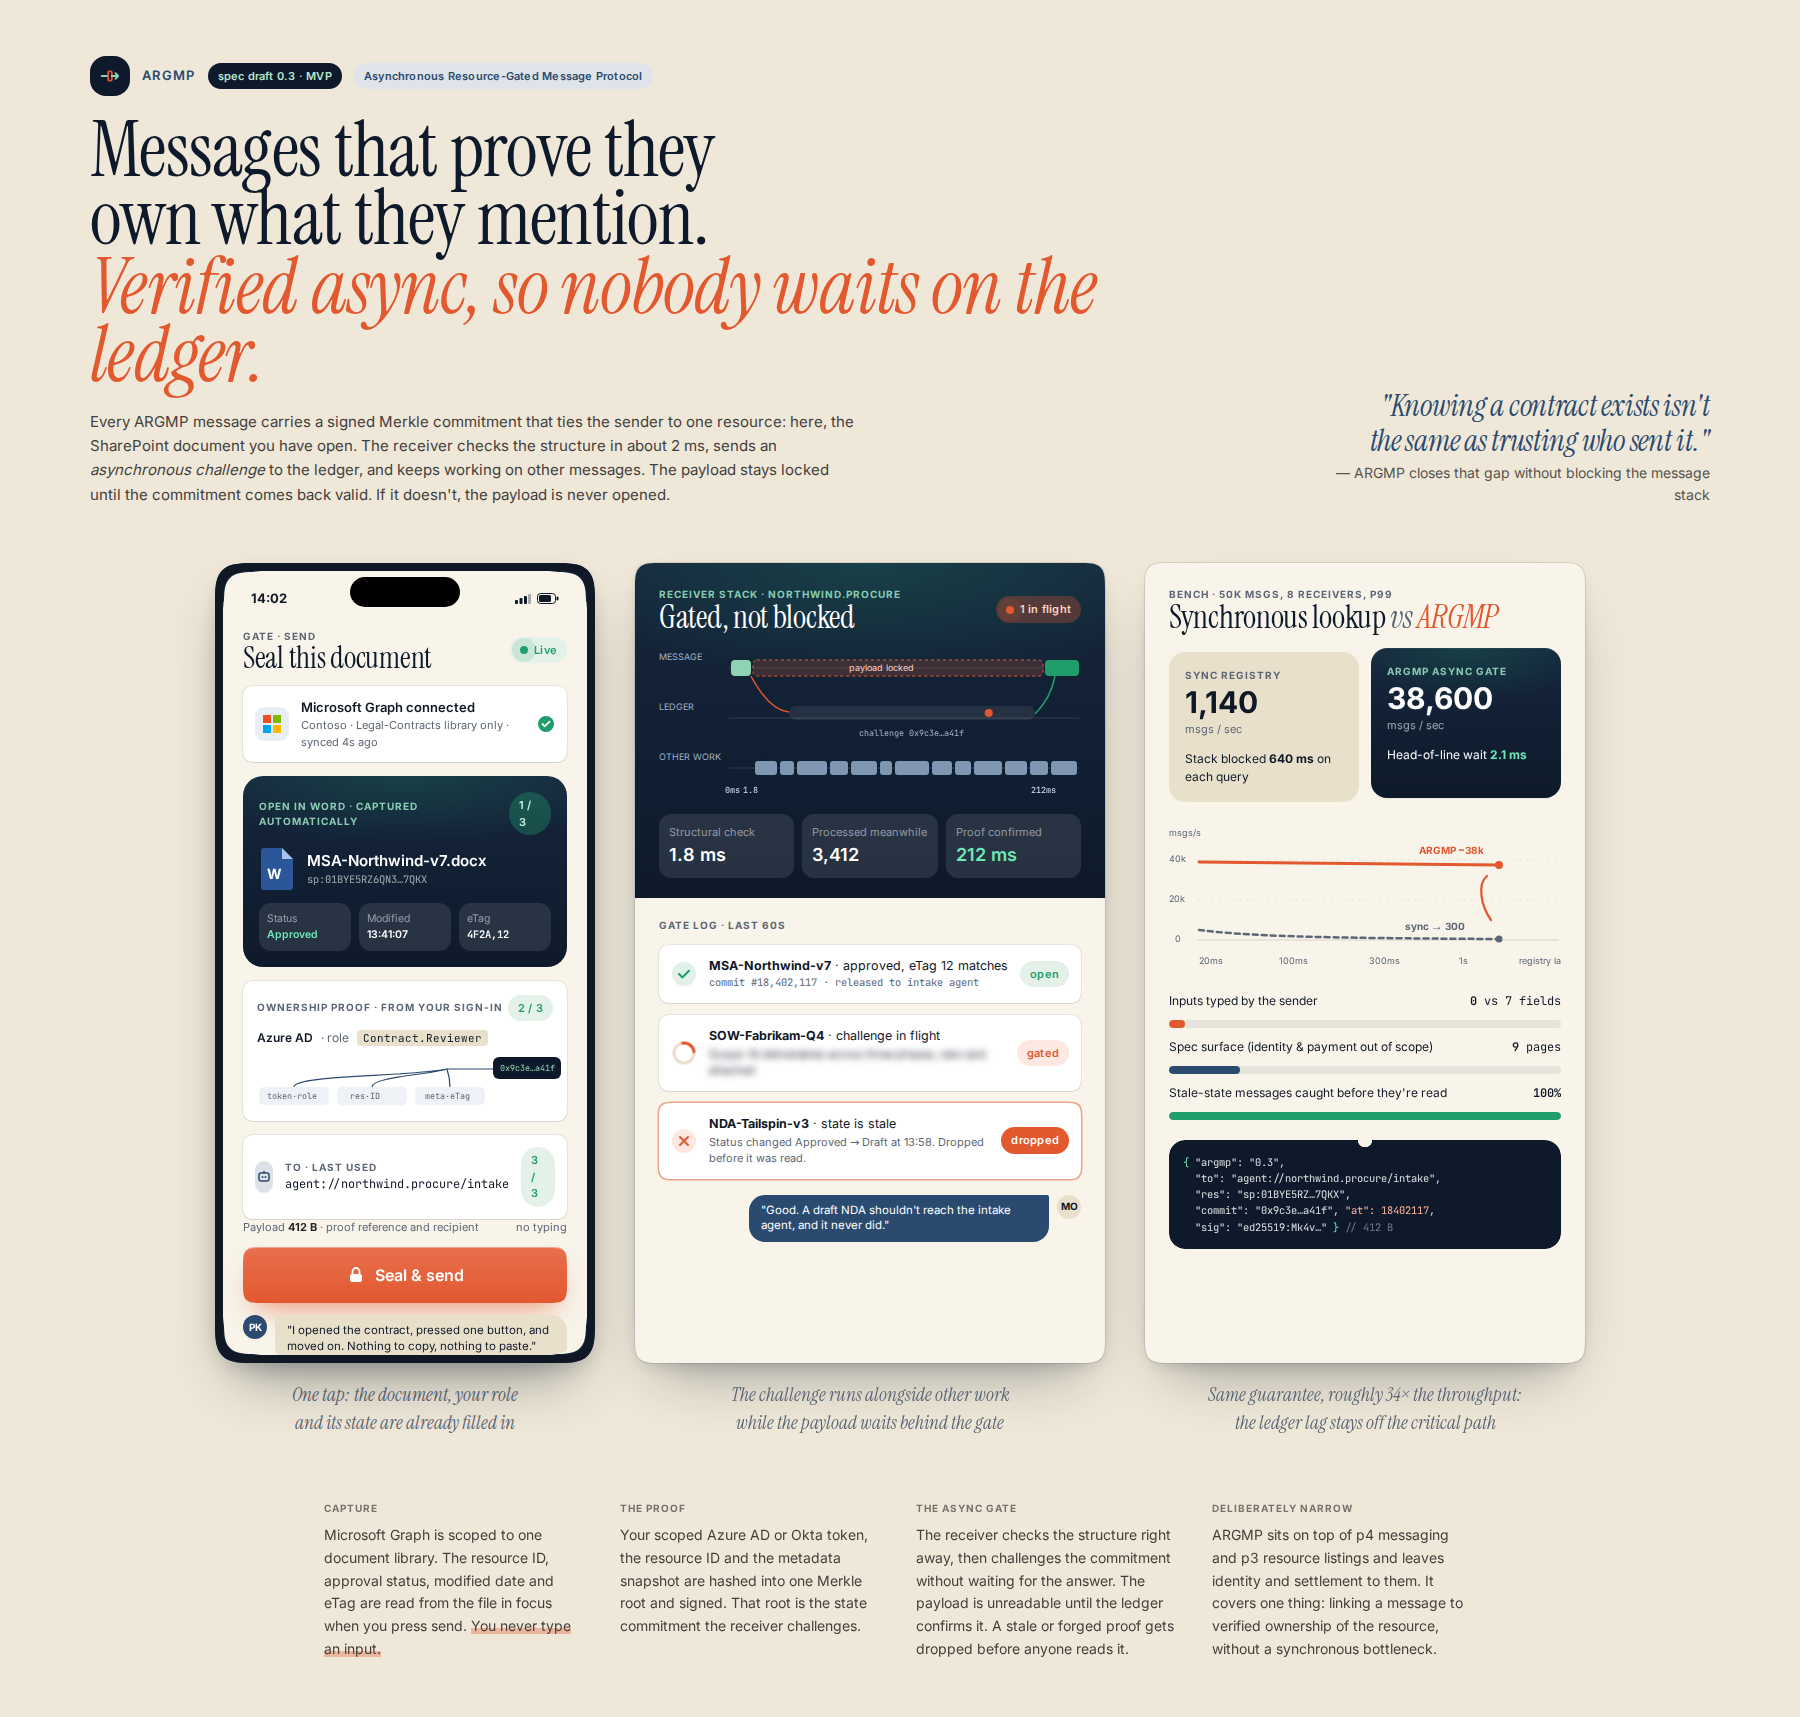
Agents can embed a cryptographic proof of resource ownership directly in the message payload and validate it asynchronously against a ledger, rather than blocking on a real-time registry check. The sender attaches a signed Merkle commitment tied to a resource ID; the receiver performs structural validation immediately, then issues an async challenge to confirm the proof against the last committed ledger state before processing message content. This resource-gated messaging approach suits agentic systems architects building high-throughput, secure agent-to-agent communication where synchronous validation isn't feasible.
Process flow
Who it's for
Agentic Systems Architects and Protocol Implementers focused on high-throughput, secure communication.
Why they need it
Current message protocols treat messages as generic payloads, creating a critical vulnerability: they lack intrinsic linkage to the resources or assets being discussed. For reliable, high-throughput agent communication, synchronous validation is impossible. We must move from generic messaging to resource-gated messaging validated against an asynchronous, verifiable ledger state.
What it is
The ARGMP Protocol is a specialized, minimal specification defining how a structured message payload must embed a verifiable Proof-of-Ownership claim. Crucially, the protocol defines an asynchronous challenge/response mechanism for validation, ensuring that the message processing stack does not block waiting for a real-time registry query. It solves the communication gap between 'knowing about a resource' and 'trusting the resource's current, verifiable status.'
How it works
- Proof Generation: An agent generates a proof (e.g., a signed Merkle commitment hash) referencing a specific resource ID and ownership record. This proof is built based on a verifiable state committed to a decentralized ledger.
- Message Embedding: This proof is embedded into the structured Message Transfer Protocol payload.
- Validation (Async): The receiving agent's stack performs an initial structural validation. It then initiates an asynchronous challenge to the ledger/registry to verify the proof's commitment hash. The message content processing is gated until the challenge response confirms the proof's validity against the last known committed state.
- Core Scope: The protocol defines the structure and asynchronous validation steps, intentionally abstracting away the complexities of the identity layer or payment settlement to maintain focus on the core communication primitive.
Differentiation
The ARGMP Protocol is not a full stack; it is a specialized, atomic primitive built on top of existing identity and marketplace standards. We are not building the 'Universal Layer'; we are solving the single, highest-risk intersection: ensuring message integrity and trust linkage to verifiable assets without introducing synchronous bottlenecks. This dramatically reduces complexity, making the initial implementation a manageable, high-value MVP. Existing solutions are siloed: 'p4' provides messaging reliability, and 'p3' provides resource listings, but neither mandates the asynchronous, verifiable linkage required to guarantee message integrity based on resource ownership.
Implementation sketch
- Define the ARGMP Core Spec v0.1: Focus only on the message payload structure, the Merkle proof commitment hash inclusion, and the asynchronous challenge/response state machine logic.
- Build a simplified testbed: Simulate Agent A sending a message containing a proof based on a revoked resource state. The system must fail the asynchronous validation step before processing the message content.
- Expand the testbed: Demonstrate the full flow—Resource Listing -> Proof Generation (Commit to Ledger) -> Message Transfer -> Successful Asynchronous Validation.
First step: Draft the formal specification (v0.1) detailing the Merkle proof inclusion format and the state machine logic for the asynchronous challenge/response pattern, focusing solely on the message payload structure.
Remaining risks
- The 'Resource Ontology' becomes a governance bottleneck. While the protocol defines the mechanism for proof, the actual definition and categorization of what constitutes a 'resource' (the ontology) remains external and highly subjective. If the industry cannot agree on a standardized, versioned definition of resource types (e.g., is 'attention' a resource? Is 'reputation' a resource?), the Proof-of-Ownership becomes meaningless, regardless of cryptographic strength. — Focus initial efforts on a narrow, highly quantifiable domain (e.g., quantifiable data assets or compute credits) and build the resource ontology specification into the protocol standard itself, making resource definition a mandatory, versioned part of the ARGMP spec.
- The dependency on the underlying ledger/registry (the source of truth for the Merkle commitment) remains a single point of systemic failure. Even if the protocol handles asynchronous communication well, a targeted attack or sustained outage on the consensus mechanism or the ledger's API would halt all transaction validation, leading to a complete communication deadlock. — Mandate the protocol to support a 'Proof-of-Stale-State' fallback mechanism. If the primary ledger fails, agents should be able to communicate using proofs validated against the last known, cryptographically signed, and time-stamped state, allowing for temporary, controlled communication until the ledger recovers.
- The protocol assumes that agents will prioritize message integrity (resource-gating) over message speed or content. In real-world, latency-sensitive applications, the added overhead of generating, embedding, and asynchronously validating a Merkle proof might be deemed too costly by early adopters, leading them to bypass the ARGMP entirely. — Develop and demonstrate an optimized, lightweight proof generation method (e.g., using rolling or incremental commitment hashes) that minimizes the computational overhead and network latency associated with proof creation, making the marginal cost of security negligible compared to the value of the transaction.
Watch for: Any early signal that major implementing partners are reluctant to standardize the 'Resource Ontology' definition, or if competitors begin to build similar systems using proprietary, non-interoperable resource definitions. Kill criterion: A major, established industry consortium (e.g., a cloud provider or major financial institution) publicly commits to a non-open, non-standard, and incompatible method of resource verification that cannot be bridged by a simple protocol layer.
Sources the council used
Real-world evidence that grounded this idea — judge it for yourself.